
Unable To Access Opcode Bytes At Rip
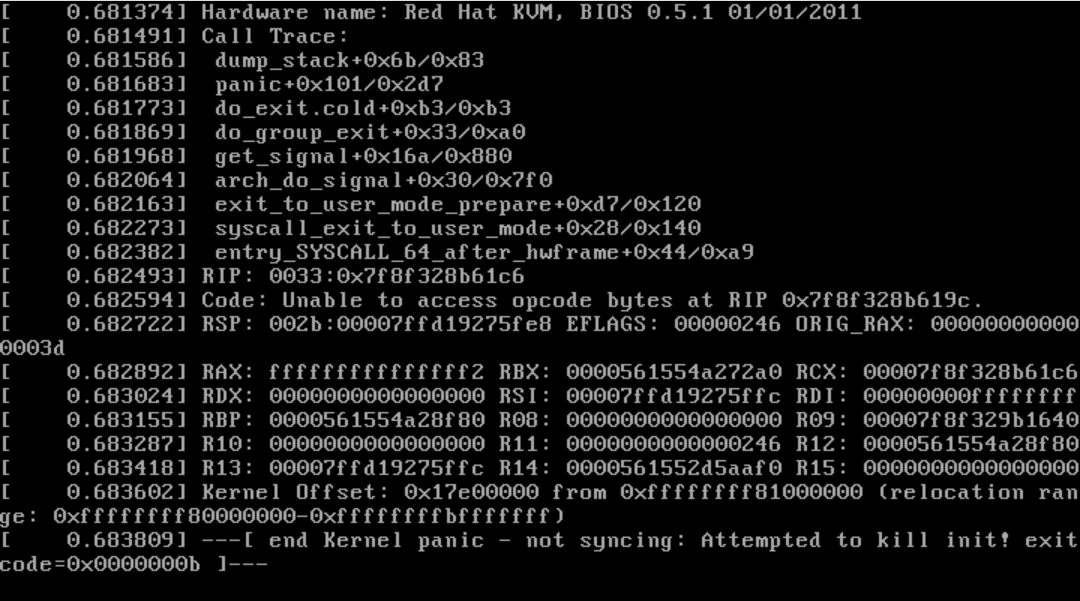
Okay, so you’re coding along, minding your own business, when suddenly your program throws a tantrum and spits out: “Unable to access opcode bytes at RIP.” Yikes. It sounds like a cryptic curse from a frustrated wizard, right? But I promise, it’s not as scary as it looks—it’s just your computer being a drama queen.
First, let’s break down that jargon. RIP isn’t “Rest In Peace” for your code (though it feels that way). In assembly language, RIP is the Instruction Pointer register—basically the pointer that says, “Hey, execute whatever instruction is at this memory address next.” And opcode bytes are just the raw machine-code commands your CPU reads. So when you can’t access those bytes, your CPU is basically saying, “I can’t see the next step!” Dramatic, but fixable.
Why Does This Happen?
Imagine you’re reading a recipe book, but someone ripped out the page you need. That’s your program trying to execute code from a memory address it doesn’t have permission to read. Maybe that address is in a different process’s memory, or you’re accidentally jumping to null—which is like trying to read a book that doesn’t exist.
Must Read
- Did Kelly Clarkson Just Get Julia Roberts Treatment? The Untold Truth Behind Brooklyn’s $15m Animatronic Bird Drama
- The 5-minute Visit That Broke The Internet: How Kelly Clarkson Sparked A $15 Million Mechanical Bird War
- Petty Revenge Or Viral Genius? Brooklyn Store Slaps $15,000,000 Tag On Molly The Bird After Kelly Clarkson Backlash
Another common culprit? Stack corruption. Your program’s stack—the little notepad where it keeps temporary notes—gets mangled, and RIP points to garbage. It’s like your recipe book suddenly printed a page that says “add unicorn tears” instead of “add salt.” Oops.
The Usual Suspects
Here’s where it gets fun. The error usually pops up because of a broken pointer or an invalid memory access. Think of it as your code wandering into a dark alley and finding a dead end. Common scenarios? Calling a function that doesn’t exist, or a buffer overflow that overwrites your return address. Classic rookie moves—but even pros hit this.
Also, debuggers sometimes cause this. If you’re stepping through code and the debugger’s memory map gets confused, it might shout at you. It’s like your GPS recalibrating and saying “recalculating… wait, you’re in a lake.”
How to Fix It (Without Losing Your Mind)
First, check your pointers. Open your debugger, inspect that RIP value, and see if it points to a valid chunk of code. Does it look like a real address (like 0x401000) or something absurd like 0x41414141? If it’s the latter, congratulations—you’ve found a buffer overflow! Time to fix that forgotten strcpy or use a safer function.
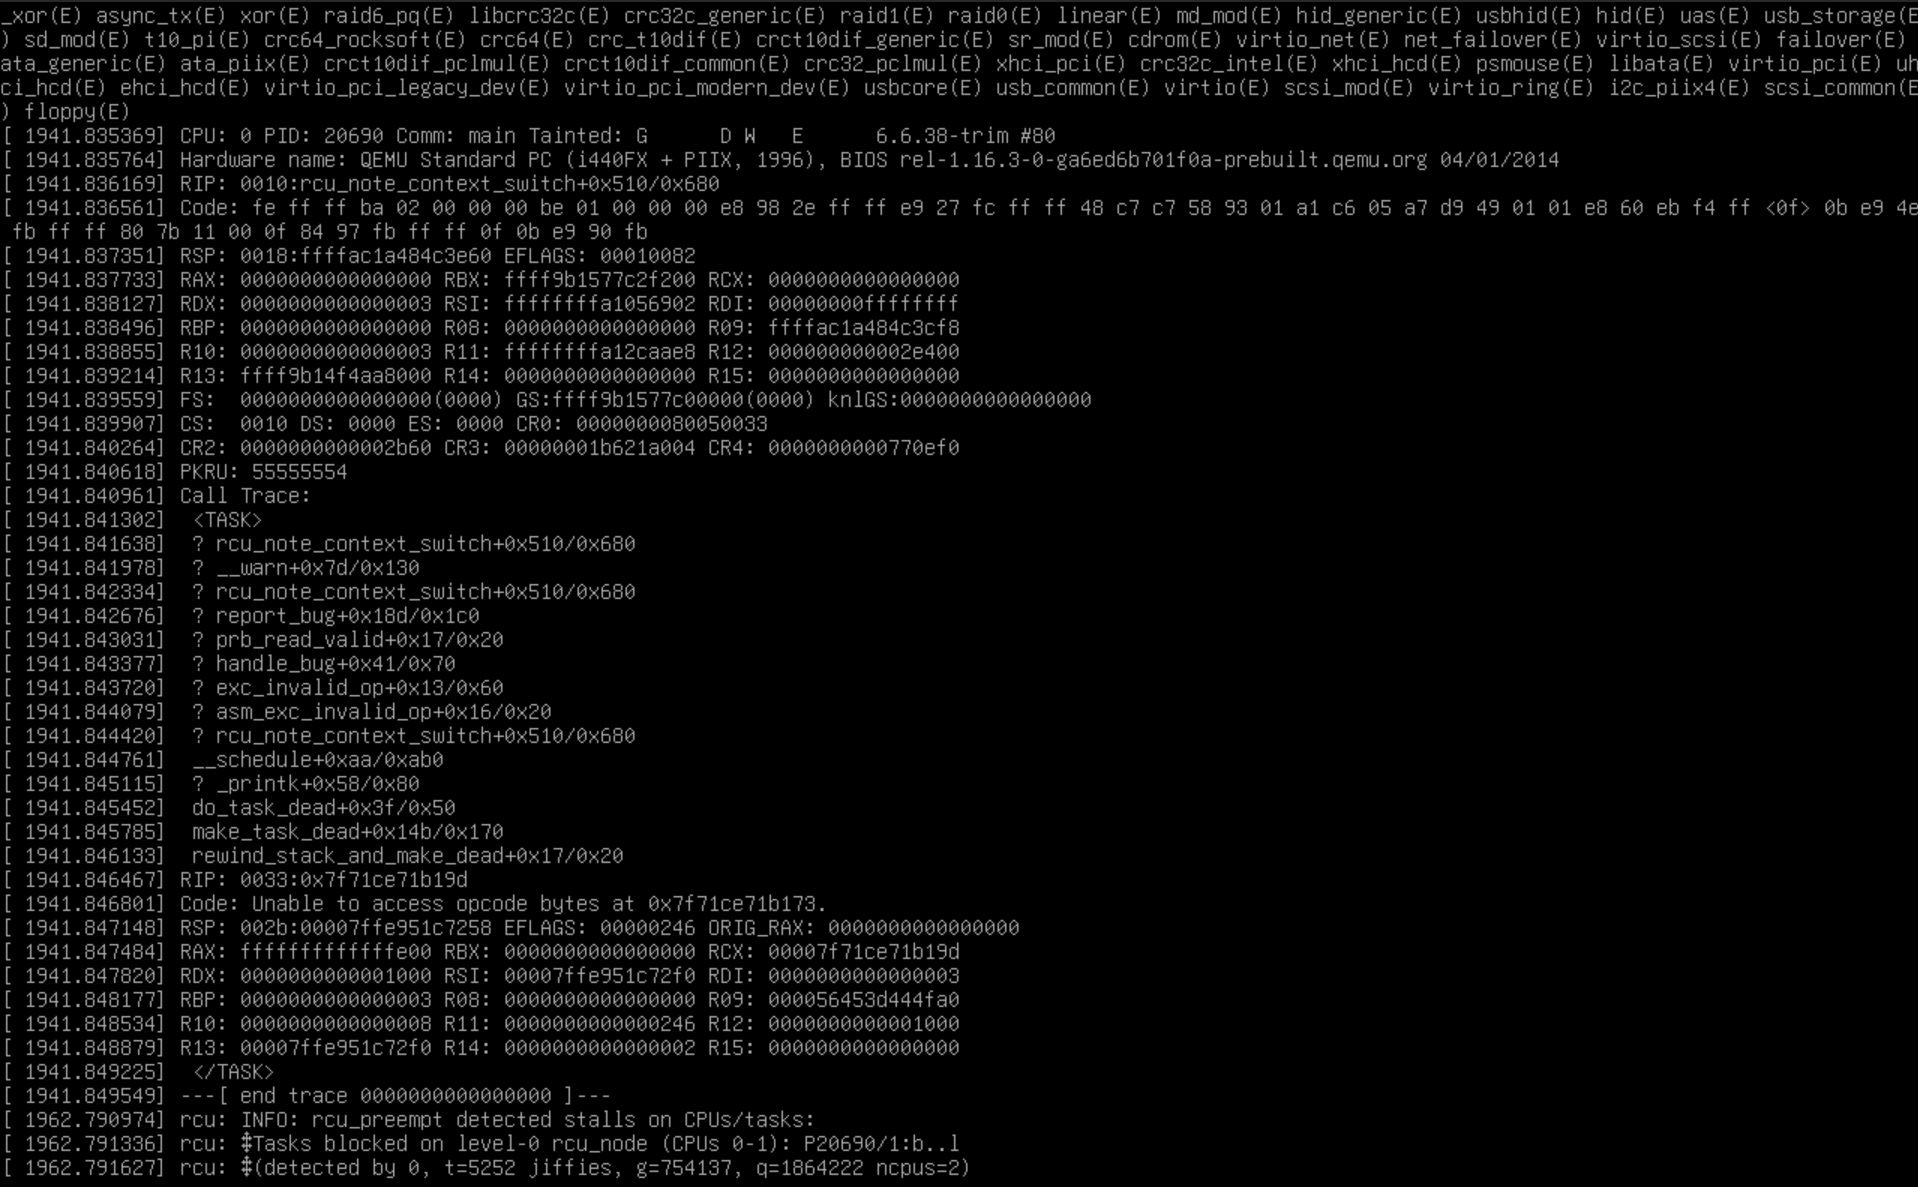
Next, verify your function calls. Are you calling a virtual function through a null pointer? Have you deallocated memory and then tried to execute it? That’s like selling your kitchen and then trying to boil pasta there. Checklist: rebuild, recompile, and double-check any custom indirect calls or jump tables.
If you’re using an optimizing compiler, sometimes it does weird things that break your assumptions. Try compiling with -O0 (no optimization) to see if the error goes away. If it does, your code might rely on undefined behavior—and that’s a party you don’t want to attend.
When All Else Fails
Google the exact error message plus your compiler or platform. Seriously, someone else has already screamed about this on Stack Overflow. I once spent three hours on this only to discover I’d accidentally set a function pointer to NULL. Three hours. Don’t be like me.
Another pro tip: use a memory debugger like Valgrind or AddressSanitizer. They’ll point to the exact line where the memory goes rogue. It’s like having a detective squint at your code and say, “Aha! Right there, you buffoon.” (In a friendly way.)

The Bigger Picture
This error is actually a gift in disguise. It stops your program from crashing in a really messy way (like corrupting your hard drive or setting your CPU on fire—okay, that’s dramatic, but still). It’s your computer’s way of saying, “Hey, I care about you, let’s not do something stupid.”
And think about it: you’re debugging at the assembly level. That’s hardcore. You’re literally talking to your processor. I bet your ancestors are proud—especially the ones who used to debug with punch cards and tears.
Uplifting Conclusion
So the next time you see “Unable to access opcode bytes at RIP,” don’t panic. Take a deep breath, sip your coffee (or tea, or liquid courage), and remember: every great programmer has seen this error. It’s a rite of passage, like tripping on stage during a speech. You get up, you fix it, and you tell the story later with a laugh.
And hey, even if you don’t fix it right away? You’re learning. You’re diving into the guts of how computers work. That’s awesome. You’re awesome. So go tackle that bug, and when you finally see your program run without the error, do a little dance. The CPU might not see it, but I’ll be cheering for you from here. 💻🎉